Is there any way of creating a stored procedure programmatically, like with curl or similar?
I have problems comprehending what the actual question is.
What product and scenario do you intend?
We’re currently running a stored procedure in Invantive Cloud, running it via Curl.
We would rather not have to update the source code for the stored procedure via the GUI for Invantive Cloud, but programmatically via curl or a similar solution.
Is that possible?
API-er for vedlikehold av Cloud-metadata
For øyeblikket finnes det ingen API-er for vedlikehold av innholdet i applikasjonsmoduler som er adresserbare for sluttbrukere. Internt bruker Invantive Cloud API-er for å registrere oppdateringene med Data Guard (se Invantive Cloud Structure).
Pakken cloud_metadata tillater noe begrenset tilgang til modullogikk, som kan utføres ved å hente mer metadata i tillegg til utførelse.
Distribusjoner
For distribusjoner på server er det mulig å bruke Invantive Data Hub eller Invantive Query Tool. De kan direkte få tilgang til de samme og til og med flere databeholdere enn Invantive Cloud.
Når det kun gjelder utviklingstid, kan Query Tool brukes til å skrive modullogikken.
Hvilken type logikk planlegger du at den skal være variabel? Eller er det for distribusjon gjennom en pipeline?
Or is it for deployment using a pipeline?
This is the case. Ideally we would like to have a CD pipeline pushing the stored procedures to invantive. So any solution that can be done programmatically would be of help here.
Thanks for the explanation. This function to change the Invantive Cloud metadata of an organization (each organization is a tenant / environment) is not yet available.
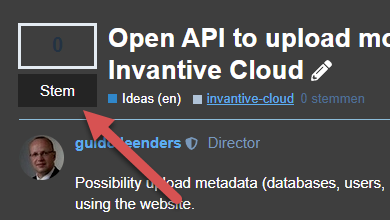
An idea has been registered: Open API to upload modules (stored procedures) and other metadata to Invantive Cloud
There is no real showstoppers, since for security reasons the backplane already uses a secured API for this. However, at that time we decided against this API to the Internet to introduce an additional layer of protection. We have seen too cases in which such an API was less secure than the vendor assumed it, leading to ta risk of massive data leaks.
When the need becomes more established, the mindset over the last months has been towards an additional API layer on the already secured API and secured back-end storage. This additional API layer provides only limited operations of the original set of operations of the backplane API.
Alright, thank you for registering the idea. Is there any way to formally support this idea?
Yes, the formal approach besides a post is to add a vote to it, see picture below. I don’t know whether the word “Stem” is translated into English in your display, but it means “Vote”.